Complade Certification Portal
Complade lets clients estimate costs, submit evidence and follow their audit online.
Support for additional standards
ISO/IEC 42001, ISO/IEC 27701 and ISO 9001 services are planned. Email certification.info@complade.com to discuss your scope and timing. Any proposed engagement will state its accreditation status before you commit.
Complade is not currently SCC-accredited for ISO/IEC 42001, ISO/IEC 27701 or ISO 9001. Assessment of these additional programmes is planned as part of Complade’s annual accreditation audit with the Standards Council of Canada in Q2 2027, from April to June. Accreditation remains subject to SCC’s assessment and decision. Approval and its timing are not guaranteed.
Current automatic estimates cover ISO/IEC 27001 and CyberSecure Canada.
Discuss a quotation by emailUse the portal to
- Get an instant estimate and submit your certification application
- Review and sign certification agreements online
- Track your application, agreements, payment status, and audit progress
- Upload Stage 1 audit evidence for your assigned auditor
- Download signed applications and agreements
Use the same email address that received your Complade invitation. Access to an organization’s certification workspace is restricted to authorized users.
Portal loginFrom application to certificate, in one portal.
Apply free, review your quotation and agreements, then decide whether to sign. Meet your audit team and agree how to share Stage 1 evidence. Pay before the auditor begins reviewing them. Screenshots below use illustrative sample data.
Explore the full audit process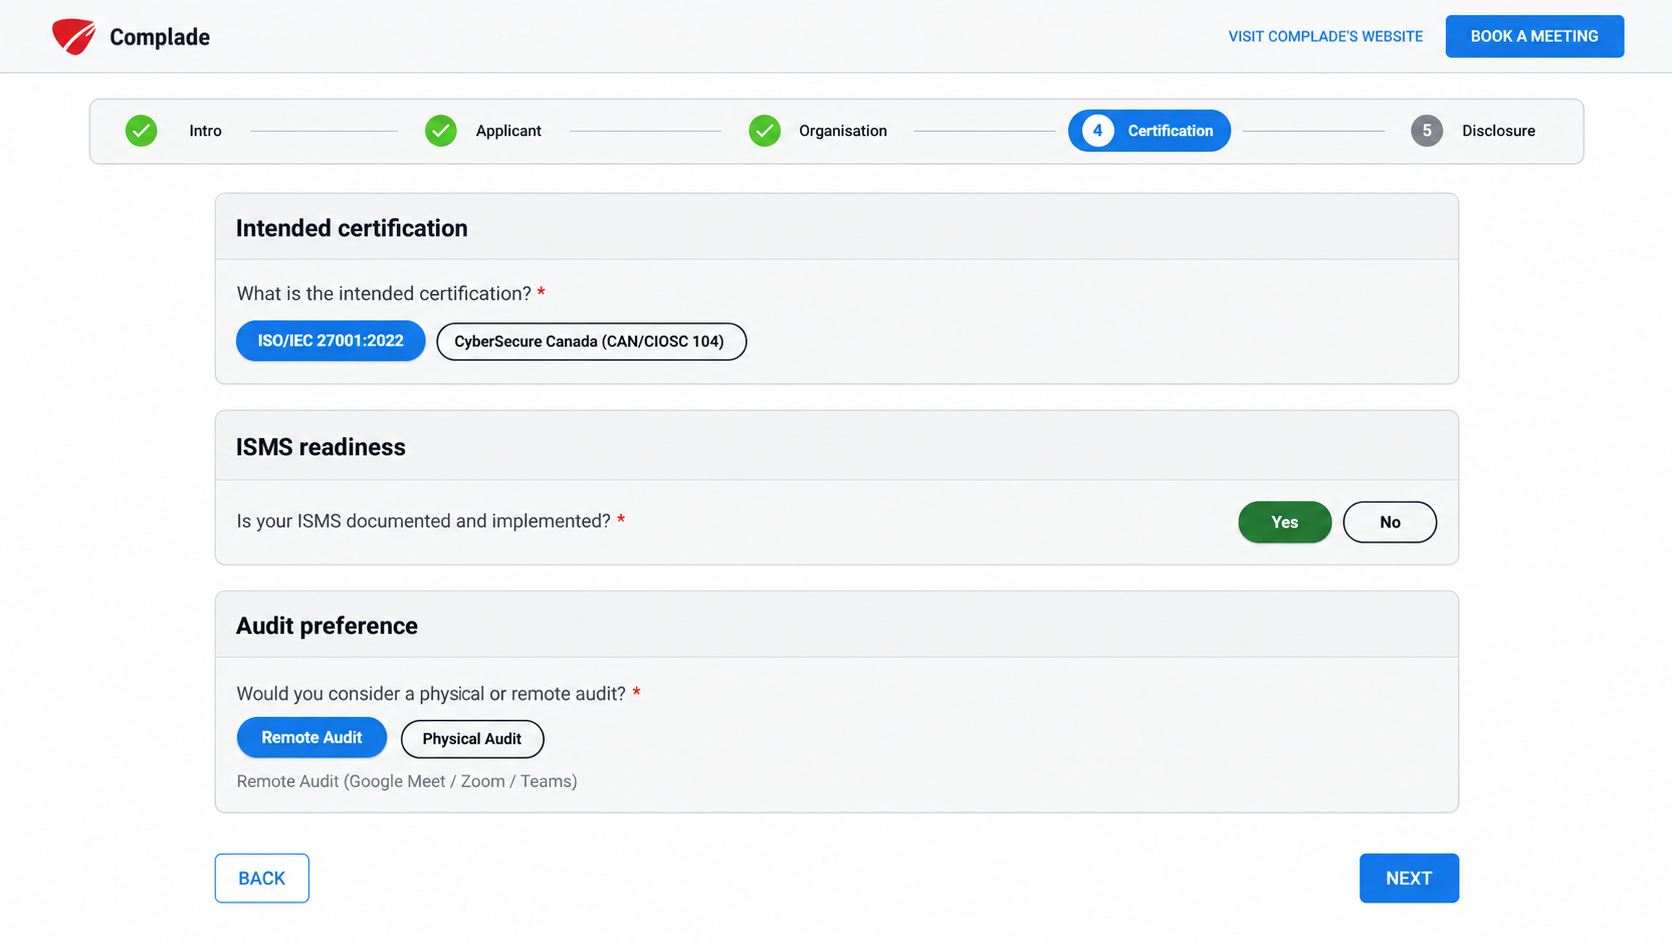
Apply free and receive an estimate. Tell us about your organization and audit preferences without committing to certification.
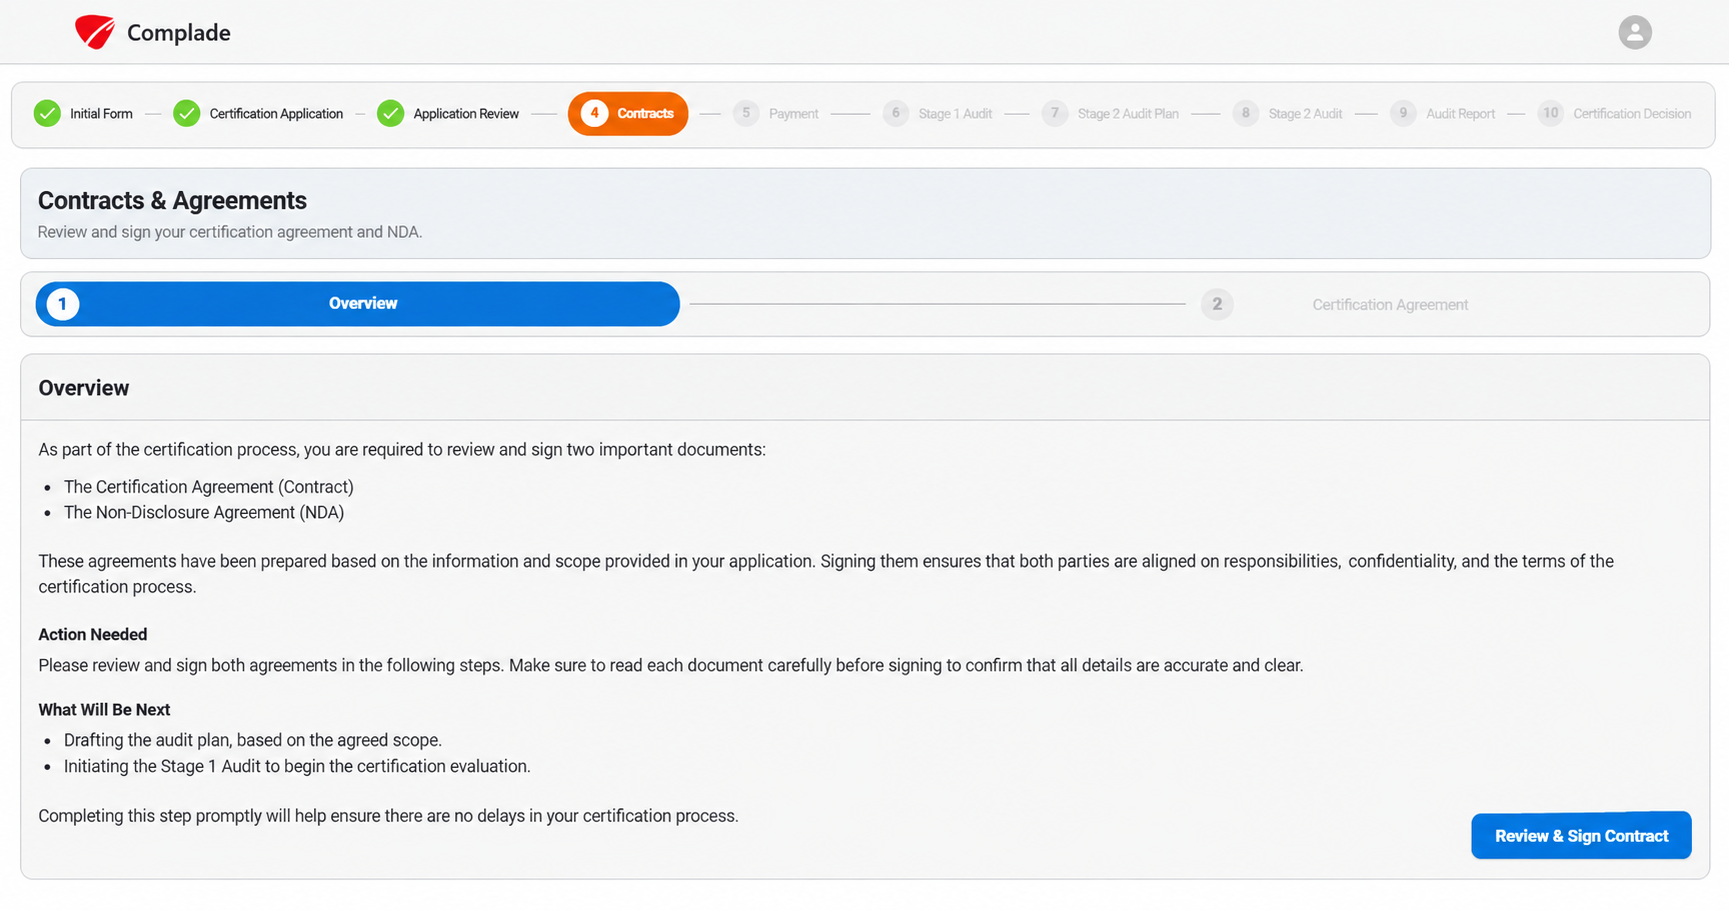
Receive confirmed pricing and audit effort after application review. Read the agreement and NDA (non-disclosure agreement) before deciding to sign.
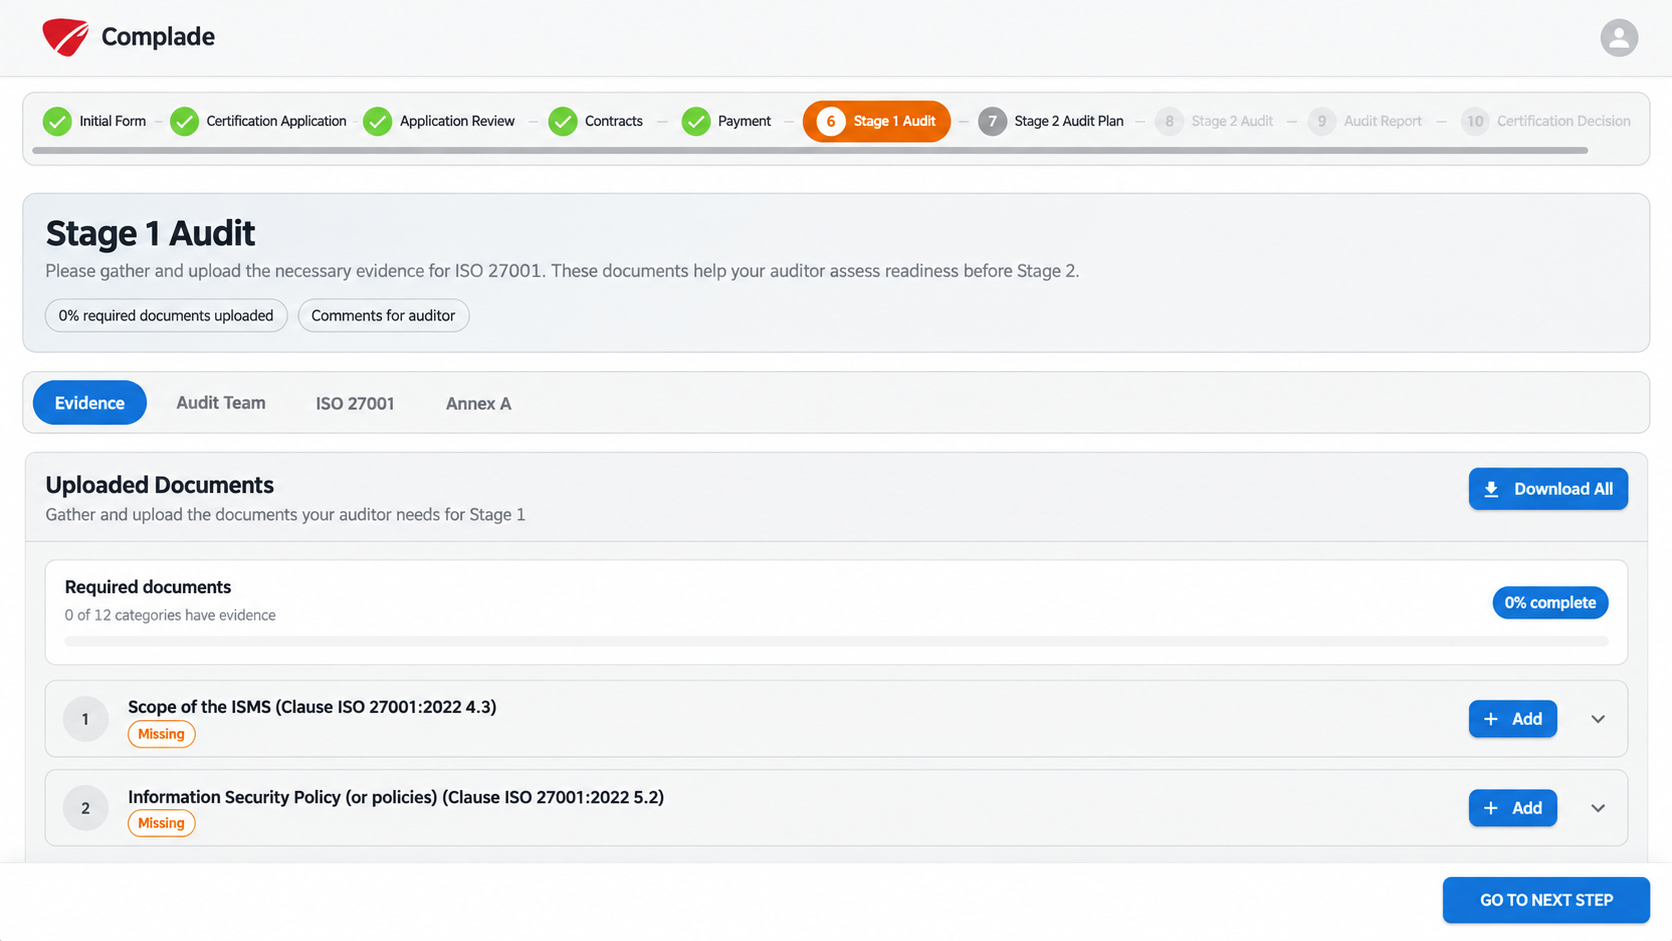
Upload required files, arrange controlled auditor access or authorize an available integration as evidence becomes ready.
Payment is due once the required evidence is available through the agreed sharing method, before the auditor begins the Stage 1 review.
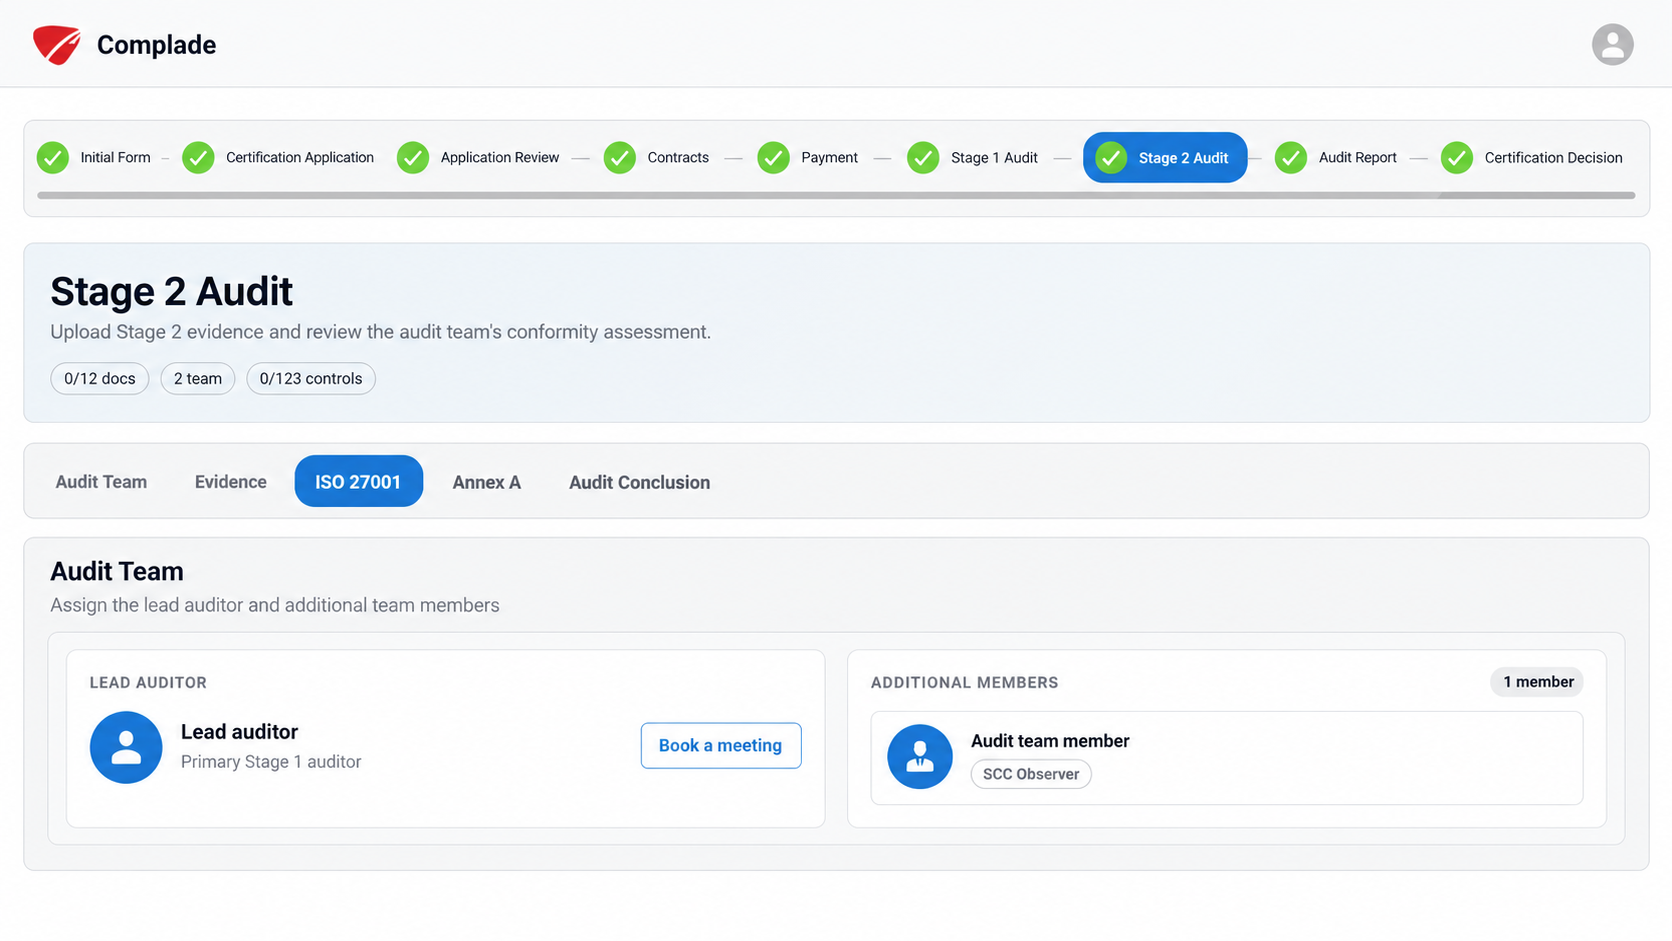
Review the audit schedule and arrange for the relevant staff to attend their sessions. The auditor evaluates implementation and effectiveness through interviews and evidence. Stage 2 duration depends on the confirmed scope and audit plan.
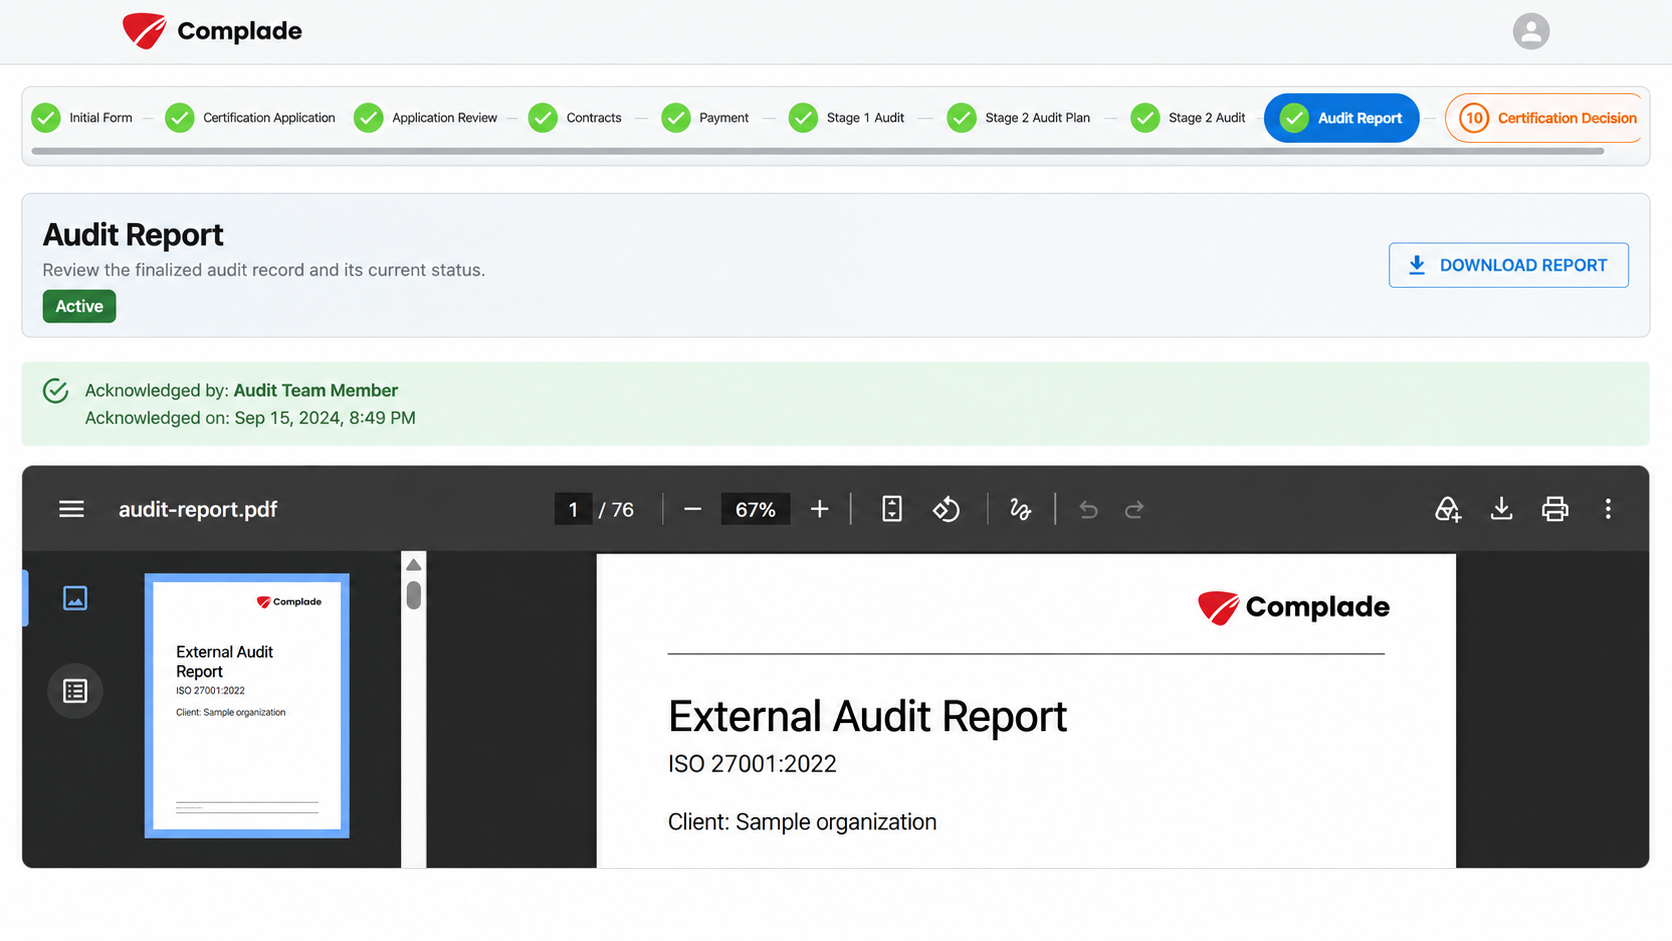
Review and download the completed report in the same workspace.
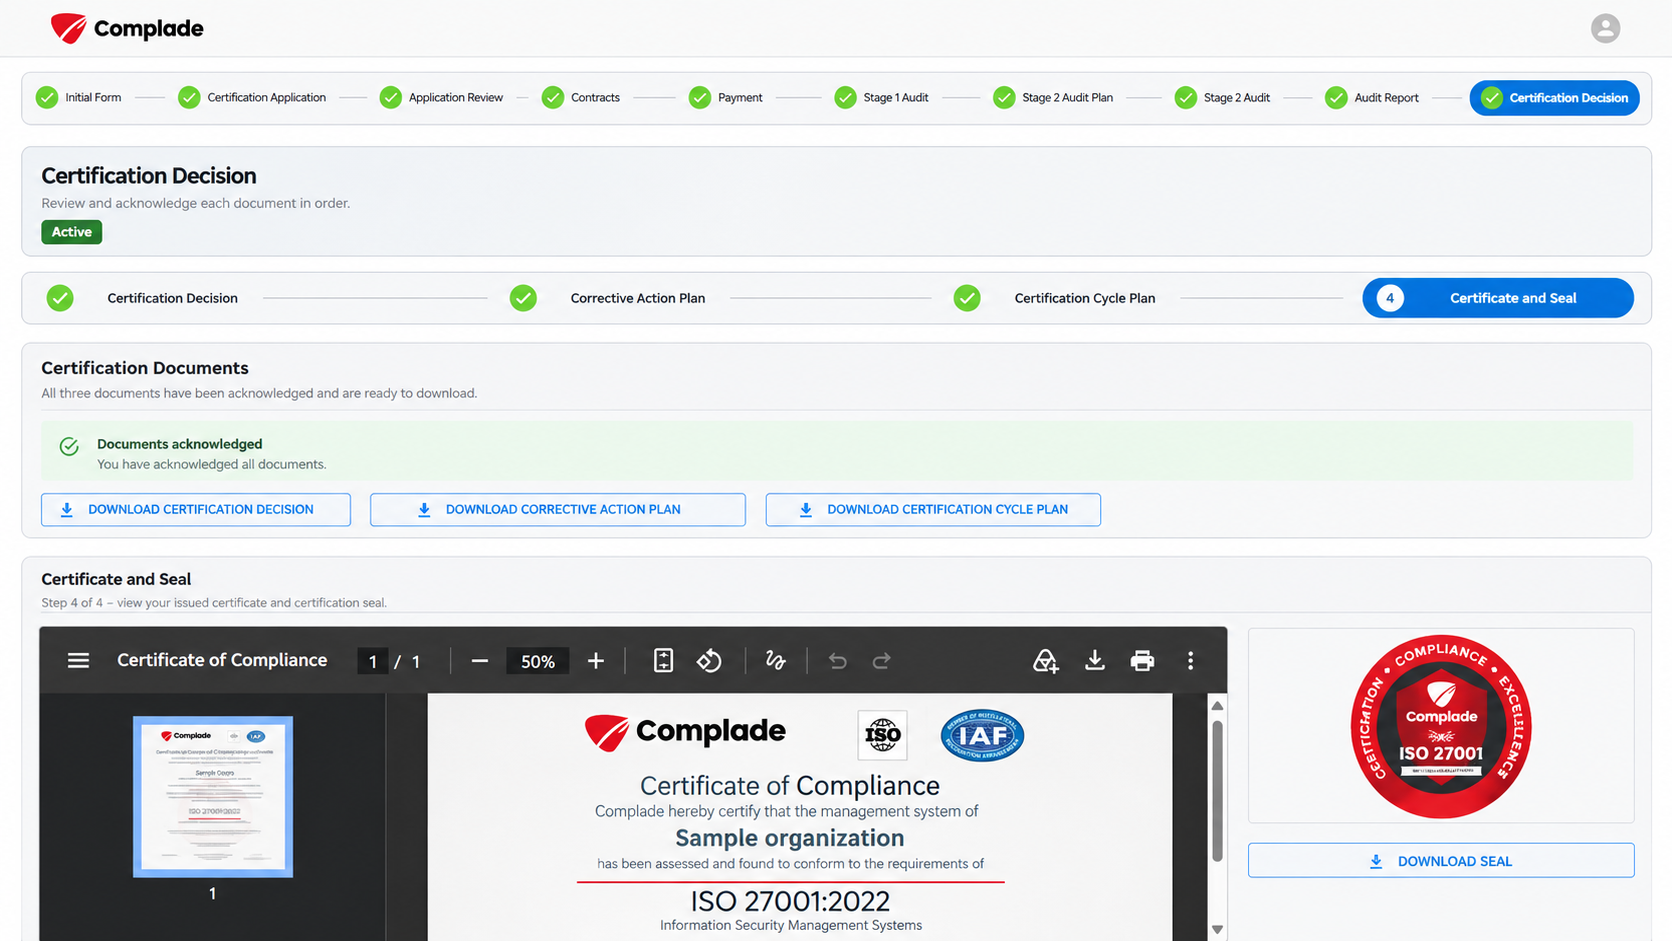
Access certification records and the certificate after independent review.
Before you share audit evidence
Can we apply while some audit evidence is still being prepared?
Yes. You can submit an application and describe your current readiness before every record is ready. Applying does not confirm readiness for certification. After scope review and signing the agreements, you can make Stage 1 evidence available through portal uploads, controlled auditor access or an available integration. The published target for initial review starts after the complete required submission and payment. Stage 1 assesses readiness for Stage 2, including internal audits and management review. Missing or ineffective activities may delay progression. Complade explains audit requirements and findings without providing implementation consulting.
View links and resources →How can we protect confidential information during the audit?
Review the mutual NDA and confidentiality terms before sharing evidence. Discuss sensitive records and access restrictions with your auditor before uploading or screen sharing. Evidence can include selected records, redacted copies or a controlled demonstration where these provide sufficient audit evidence. Do not upload passwords, private keys or access tokens. Auditors need enough evidence to support their conclusions; some records may contain personal or commercially sensitive information. Agree a suitable way to review it rather than assuming that all sensitive information can be excluded.
View links and resources →Your audit evidence, without the email trail.
Complade does not accept audit evidence by email.
Share existing policies, procedures and system records through controlled auditor access, an available integration or direct upload to the Complade Audit Portal. Keep evidence out of unmanaged email threads and reduce duplicate preparation.
Use your governance, risk and compliance (GRC) tool or give access to SharePoint, OneDrive, Google Drive, Confluence or Notion. You can also upload Word, Excel and PDF files during the Stage 1 desk review.
See evidence sharing options and integrations
Add Complade as your auditor in Vanta
A GRC subscription is optional. Every sharing method is subject to the same audit criteria. Access to a tool or a successful evidence transfer does not establish conformity or guarantee certification.
Coming soon
- DrataComing soon
- SprintoComing soon
- ServiceNow GRCComing soon
- OneTrustComing soon
Start your certification application
For ISO 27001 and CyberSecure Canada, your application starts in the portal. Review our proposal before signing or paying.
Not ready for your audit yet?
Review the requirements and evidence examples for your certification. You can start a free application while preparing and update it later.
Take the optional self-assessment. Download your report, then book a free one-hour discussion of your results.
Your estimate is a useful pricing guide. The final price is usually close to it when your scope, application details and pricing assumptions remain the same, although the estimate is not a guaranteed price.
For ISO 27001, a firm quotation and agreement for your review can only be prepared once your information security management system (ISMS) is implemented and you know your exact scope statement and application details. Complade then reviews those details and the required audit time before confirming the price.
You can start your application while preparing, then explore our Audit preparation guides. When you are ready, log in to the portal and update your application with your final scope and current details. You can then review the firm quotation and agreement before deciding whether to sign.
Apply free and receive an estimate
Describe your organization and scope. Your application is non-binding.
Review your quotation and agreements
Once you are ready and your scope is confirmed, Complade reviews your completed application and confirms audit days, pricing, the agreement and NDA (non-disclosure agreement).
Sign and meet your audit team
Choose whether to sign, then agree how to share evidence and book time with your lead auditor.
Pay before the Stage 1 review
Payment is due once the required evidence is available to the auditor, before review, unless other terms are agreed.
Questions about steps, timing or costs? Check our audit process and frequently asked questions (FAQ) for an answer. If you still need help, email us. To discuss your organization’s readiness, complete the self-assessment first. To confirm ISO 27001 or CyberSecure Canada audit days and pricing, complete the free application. For another standard, email for a quotation.