Complade certification audit process
Complade documents each stage from application review through independent certification decision and annual surveillance.
What the certification workflow looks like
From the first application to corrective actions, each step is tracked in one place. Screenshots show illustrative sample data.
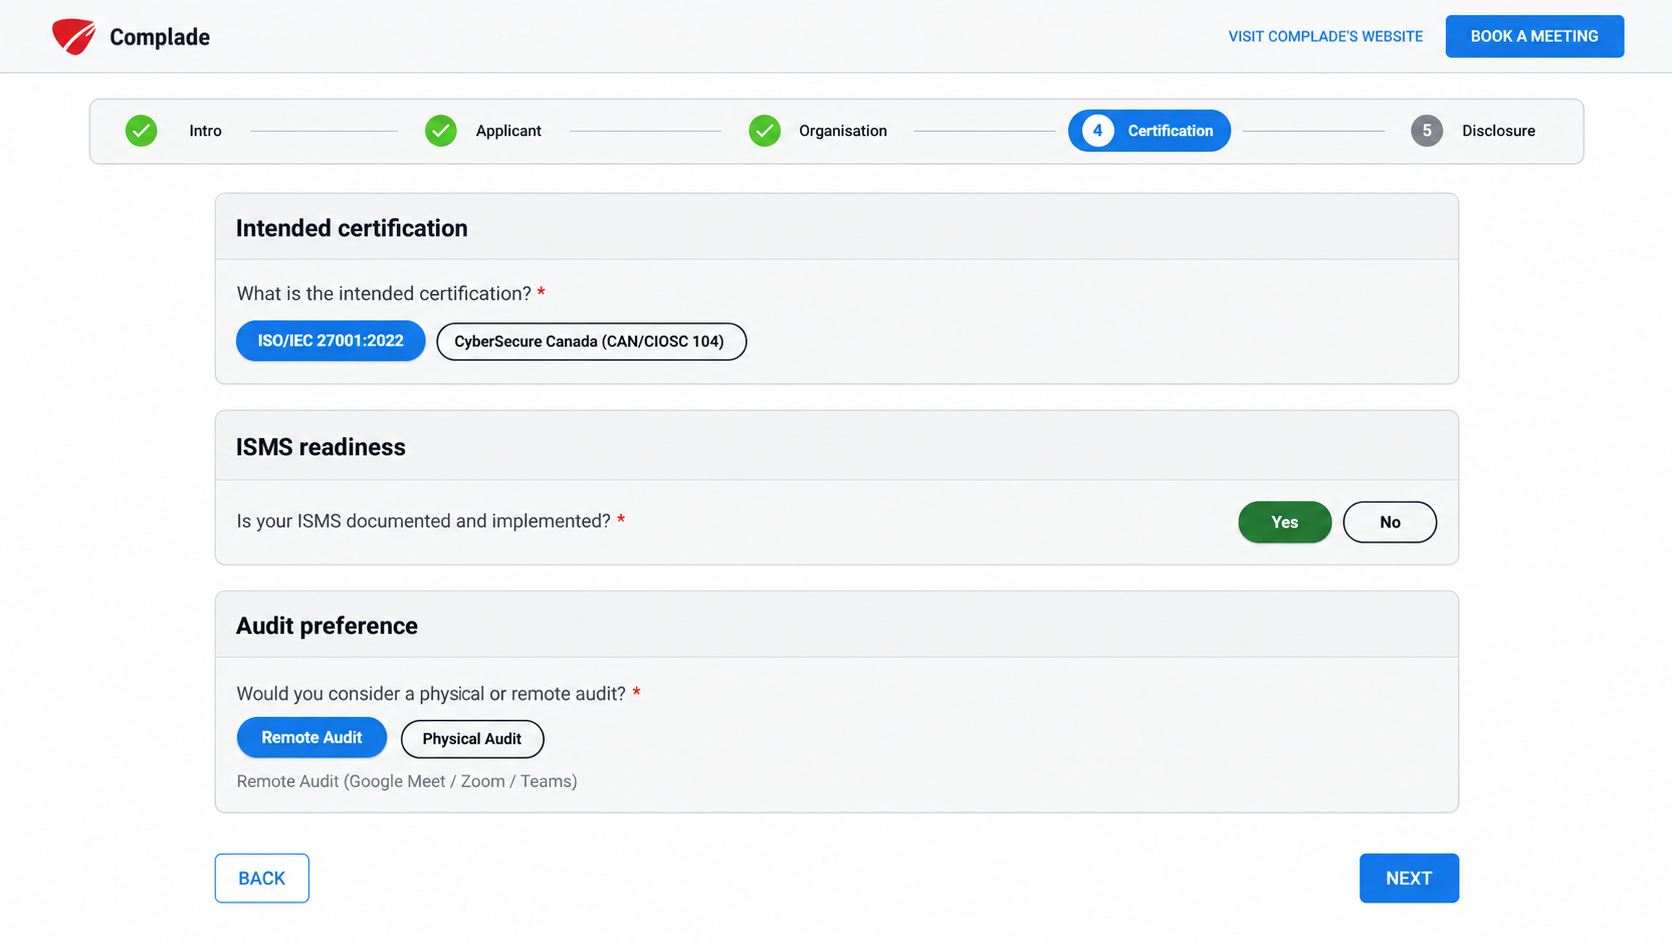
The intake records the certification sought, management system readiness and audit delivery preference.
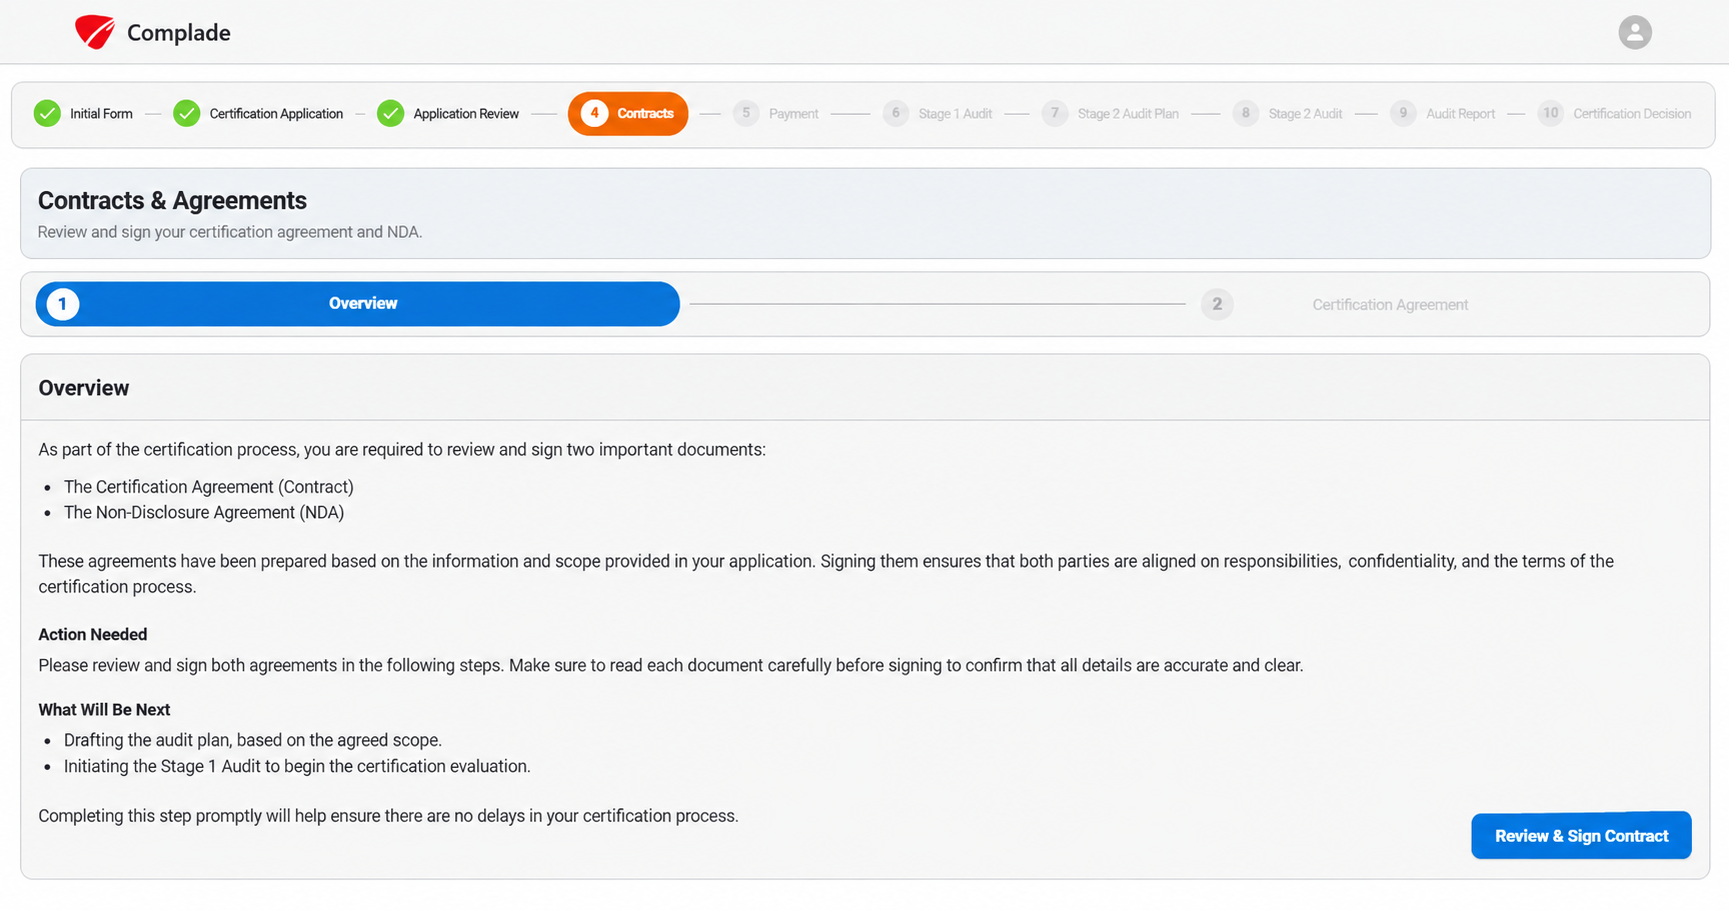
Review the certification agreement and confidentiality terms based on the confirmed scope.
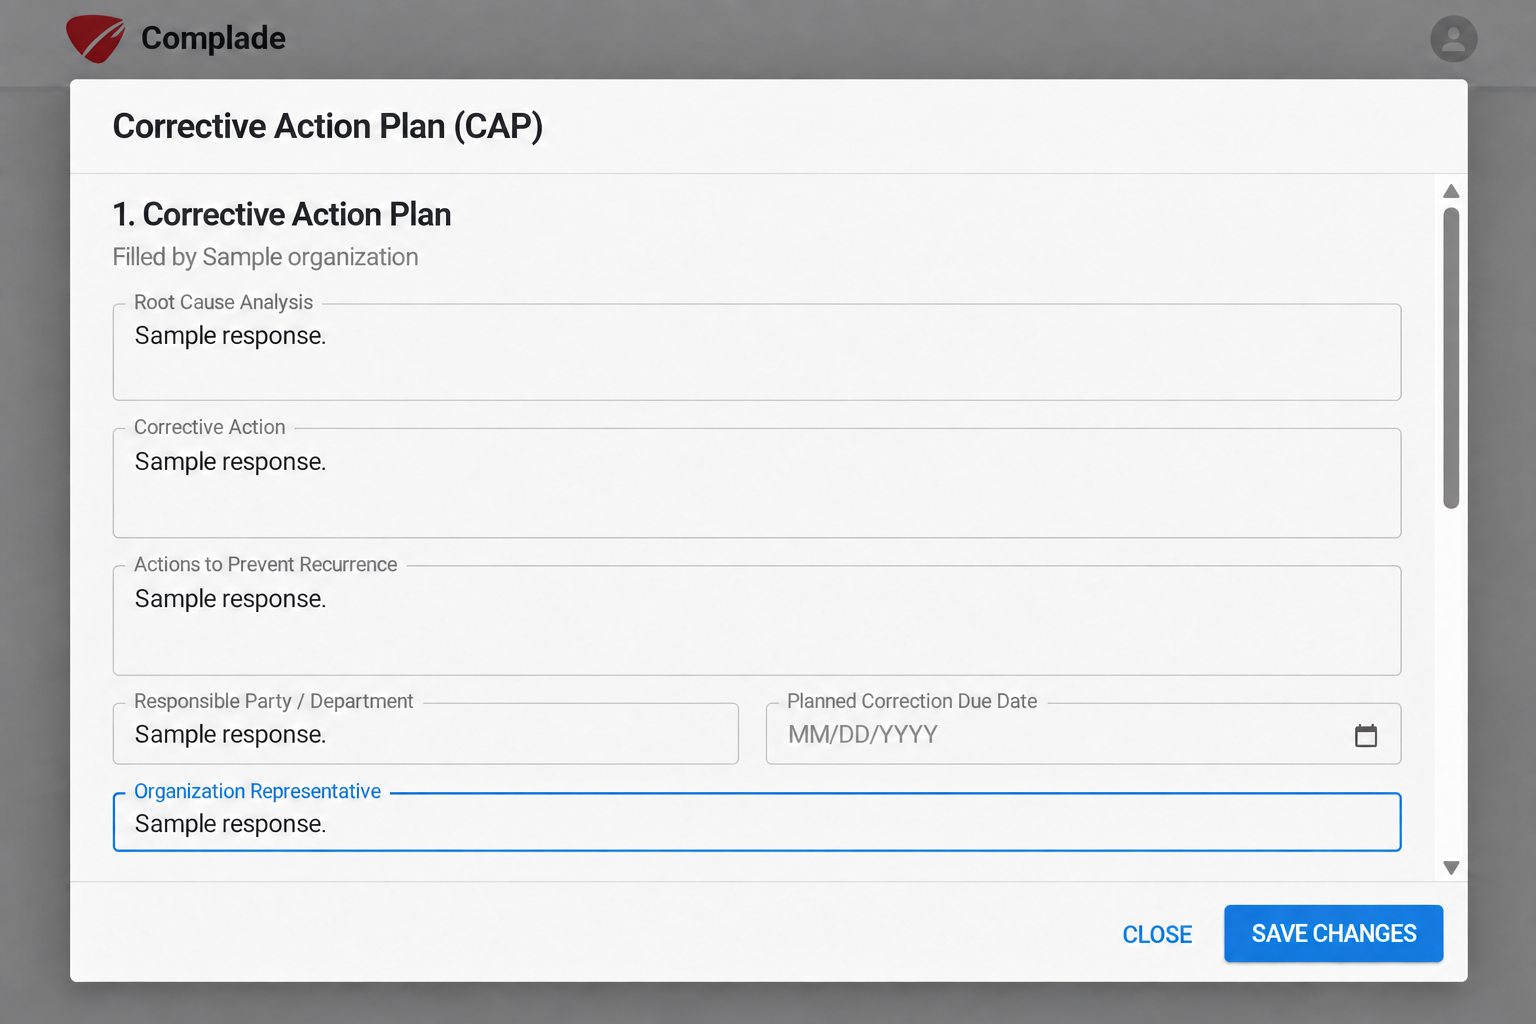
Record the root cause, corrective action, owner and supporting evidence in the portal.
Understand the audit steps
Can we apply while some audit evidence is still being prepared?
Yes. You can submit an application and describe your current readiness before every record is ready. Applying does not confirm readiness for certification. After scope review and signing the agreements, you can upload Stage 1 documents as they become available. The published target for initial review starts after the complete required submission and payment. Stage 1 assesses readiness for Stage 2, including internal audits and management review. Missing or ineffective activities may delay progression. Complade explains audit requirements and findings without providing implementation consulting.
View links and resources →What is the difference between Stage 1 and Stage 2?
Stage 1 reviews the management system's scope, documented information and readiness for the implementation audit. Stage 2 evaluates whether the management system and applicable controls are implemented and operating effectively in practice through interviews, records, sampling, observation and technical evidence.
View links and resources →What happens if the audit identifies a nonconformity?
The report records the requirement, evidence and finding. You provide correction, root-cause analysis and corrective action within the deadlines communicated. Major nonconformities require verification of correction and corrective action before certification. For minor nonconformities, review and acceptance of the plan for correction and corrective action are required before the decision, with appropriate follow-up. Classification depends on the impact on the system. A missing internal audit or management review must not be assumed to be minor. Additional verification may be needed; a full repeat audit is not automatically required. The certification decision remains independent.
View links and resources →What happens after the initial certificate is issued?
Certification is maintained through scheduled surveillance audits. For ISO/IEC 27001, surveillance audits occur during Years 1 and 2, followed by recertification before the next three-year cycle. Surveillance verifies that the management system remains implemented, maintained and effective. Surveillance follows a risk-based audit programme and sampling. A lower surveillance fee does not mean a random review of half the controls.
View links and resources →One place to manage and follow your certification.
The portal handles more than applications and contracts. It is where clients submit evidence, plan the audit, see evaluated audit points, manage corrective actions and receive reports and certification records.
- 01
Apply and contract
Complete the application, review the estimate, sign the certification agreement and mutual NDA (non-disclosure agreement), and manage certification contacts online.
- 02
Complete Stage 1
Upload required management-system documents before payment is due. Pay before the review begins. The target for initial feedback is three business days after a complete submission and payment. Respond to findings and resubmit evidence for up to three review cycles; completing Stage 1 depends on readiness and any further evidence required.
- 03
Plan Stage 2
Work with the lead auditor on dates and a detailed schedule down to each clause or control. Add the people from your organization who will attend the relevant interviews and book meetings through the portal.
- 04
Follow the audit
See each audit point, evidence request and recorded note. The result appears once the audit team evaluates that point.
- 05
Manage corrective action
Record corrections, root-cause analysis and corrective-action plans directly in the portal. Assign owners, upload supporting evidence and track review and closure.
- 06
Receive the decision
Access the Stage 2 report in the portal within two days of audit completion. Following independent certification review, receive the decision, certificate and applicable IAF CertSearch link in the same system.
Every conclusion is tied to the standard and the evidence.
Complade's ISO/IEC 27001 certification activities follow applicable requirements for accredited management-system certification bodies, including ISO/IEC 17021-1 and ISO/IEC 27006-1. The audit methodology is informed by ISO 19011, ISO/IEC 27007 and ISO/IEC TS 27008.
Organizations are certified against ISO/IEC 27001 or CAN/DGSI 104. The other documents govern or inform how certification and auditing are performed.
Preparing for audit
Complade explains the standard, application process and audit requirements. Your organization remains responsible for implementing its management system and preparing evidence. To preserve impartiality, Complade does not provide implementation consulting or internal audit services.
Initial certification
- Application intake: Complete the online application. Scope, audit time, plan and contract details are determined.
- Agreement: Review and sign the certification agreement and mutual NDA (non-disclosure agreement). Start uploading required Stage 1 documents. Payment is due before the auditor begins the review.
- Stage 1: The auditor reviews the management system and supporting evidence, then reports readiness findings.
- Stage 2: Implementation and effectiveness are tested remotely or in person.
- Corrective action: The client responds to identified gaps.
- Certification decision: A separate reviewer examines the complete audit package.
Surveillance and recertification
For ISO/IEC 27001, surveillance audits in Years 1 and 2 assess continued conformity and effectiveness. A recertification audit is required before the three-year certificate expires. CyberSecure Canada maintenance and renewal requirements are confirmed in its certification agreement.
For ISO/IEC 27001, Complade schedules the first surveillance audit within 9 to 12 months of the initial certification decision. If it is not completed by the 12-month mark, the certificate may be temporarily suspended. If the process is not completed within 6 months of suspension, the certificate will be withdrawn.
How long does it take?
Approximately six weeks is the fastest published scenario for an audit-ready ISO/IEC 27001 organization.
Timing depends on organization size, complexity, readiness, auditor availability, clarifications, and whether nonconformities must be resolved.
Not ready yet?
You can use the general audit resources while preparing, or engage an independent implementation consultant. Complade does not recommend a particular consultant or make certification conditional on using one.
Start your certification application
For ISO 27001 and CyberSecure Canada, your application starts in the portal. Review our proposal before signing or paying.
Not ready for your audit yet?
Review the requirements and evidence examples for your certification. You can start a free application while preparing and update it later.
Take the optional self-assessment. Download your report, then book a free one-hour discussion of your results.
Your estimate is a useful pricing guide. The final price is usually close to it when your scope, application details and pricing assumptions remain the same, although the estimate is not a guaranteed price.
For ISO 27001, a firm quotation and agreement for your review can only be prepared once your information security management system (ISMS) is implemented and you know your exact scope statement and application details. Complade then reviews those details and the required audit time before confirming the price.
You can start your application while preparing, then explore our Audit preparation guides. When you are ready, log in to the portal and update your application with your final scope and current details. You can then review the firm quotation and agreement before deciding whether to sign.
Apply free and receive an estimate
Describe your organization and scope. Your application is non-binding.
Review your quotation and agreements
Once you are ready and your scope is confirmed, Complade reviews your completed application and confirms audit days, pricing, the agreement and NDA (non-disclosure agreement).
Sign and meet your audit team
Choose whether to sign, then upload documents and book time with your lead auditor.
Pay before the Stage 1 review
Payment is due after the required documents are uploaded, before auditor review, unless other terms are agreed.
Questions about steps, timing or costs? Check our audit process and frequently asked questions (FAQ) for an answer. If you still need help, email us. To discuss your organization’s readiness, complete the self-assessment first. To confirm ISO 27001 or CyberSecure Canada audit days and pricing, complete the free application. For another standard, email for a quotation.
One organization, an integrated management system
ISO/IEC 27001 remains our core service. ISO/IEC 42001 and ISO/IEC 27701 also address AI and privacy risks, with requirements of their own. ISO 9001 addresses the quality of products and services. Each standard can be used on its own or integrated with the others.
It is the same organization and its context. Where activities overlap, governance and common information can be shared. One internal audit programme and a joint management review can cover the integrated system, provided the requirements, competence, results and decisions needed for every standard are addressed. The scopes may differ and must remain explicit.
Complade reviews the degree of integration before planning a combined audit. Required audit hours and competence remain specific to each standard. Your organization arranges its internal audits; Complade provides independent certification.
Support for additional standards
ISO/IEC 42001, ISO/IEC 27701 and ISO 9001 services will start on 1 January 2027. Support for these standards is being added to the portal after the holiday break. For these standards, request a quotation by email. Current automatic estimates cover ISO/IEC 27001 and CyberSecure Canada.
Email for a quotation