ISO/IEC 42001
Artificial intelligence management system (AIMS)
View the service Portal login
Complade is a Standards Council of Canada (SCC)-accredited Canadian certification body providing independent assurance through management system certification.
To make the informed assurance about the balance of organizations’ risks and controls accessible to organizations’ stakeholders worldwide.
We envision a world where resources are managed sustainably for the benefit of all.
Complade automatically contributes 0.5% of every client payment processed through Stripe to Stripe Climate, which supports emerging carbon removal technologies. Our contribution grows with every payment.
View our climate commitment →ISO/IEC 27001 remains at the core of our work. We are streamlining its process to provide it at scale while maintaining audit quality and impartiality.
ISO/IEC 27001 remains at the core of our work. From 1 January 2027, Complade will also offer certification for AI, privacy and quality management systems.
Artificial intelligence management system (AIMS)
View the servicePrivacy information management system (PIMS)
View the serviceQuality management system (QMS)
View the serviceISO 45001 and other management system certifications remain under consideration. SOC 2 is also part of our plans. It is an attestation service separate from ISO certification. These other services are not currently offered.
Complade applies its impartiality policy to every audit. The policy addresses conflicts of interest and requires consistent evaluation regardless of the organization’s size.
The SCC (Standards Council of Canada) Accreditation Symbol is an official symbol of the Standards Council of Canada and is used under licence.
Complade Inc. is a certification body accredited by the Standards Council of Canada under the Management Systems Accreditation Program. SCC (Standards Council of Canada) participates in the applicable International Accreditation Forum multilateral recognition arrangements.
Complade's accreditation scope is based on ISO/IEC 17021-1:2015 and ISO/IEC 27006-1:2024, with applicable IAF (International Accreditation Forum) mandatory documents including IAF (International Accreditation Forum) MD 4:2023.
Accreditation status and scope should be verified using Complade's current IAF CertSearch record and SCC (Standards Council of Canada) accreditation directory entry.
Complade is accredited by the Standards Council of Canada (SCC), a Government of Canada Crown corporation. SCC assesses certification bodies against the international requirements applicable to their work. ISO’s profile of SCC
View Complade’s official SCC (Standards Council of Canada) and IAF CertSearch records.
Understand the roles of SCC (Standards Council of Canada), Global ACI and Complade
Read independent SCC (Standards Council of Canada) coverage of Complade and accreditation, plus Complade’s ISO 27001 analysis published by the Cloud Security Alliance.
An SCC (Standards Council of Canada) feature about Complade and the role accreditation plays in building trust in certification services.
Read the sourceSCC (Standards Council of Canada) explains how accredited services help small and medium-sized businesses build trust, access markets and grow.
Read the sourceAn analysis of ISO 27001 certification and cloud security written by Yehia (Ian) Ahmed of Complade and published by the Cloud Security Alliance.
Read the sourceCanadian foundation. International reach.
Complade delivers ISO/IEC 27001 certification audits for organizations in Canada and internationally. Our portal brings applications, agreements, evidence and results together. Remote delivery is confirmed according to scope, locations and access to evidence.
SCC (Standards Council of Canada) accreditation attests to Complade’s competence and impartiality within its accredited scope. Multilateral arrangements support recognition of accredited certification across borders. Recognition depends on the standard and recognized scopes, rather than simply the country where a certificate is issued.
The recognition framework formerly administered through the IAF (International Accreditation Forum) MLA (multilateral recognition arrangement) now falls under Global ACI. Recognition supports international acceptance; specific legal, regulatory and customer procurement requirements still apply.
How multilateral recognition works · Recognized accreditation bodies · Complade’s accredited scope
Discuss your scope and locationsProfessional accountability
Our role is to provide informed assurance about risks and controls. Responsibility for managing them remains with your organization.
Teams are selected for the scope, required competence and availability. Conflicts of interest are reviewed before assignment.
Auditor requirementsAuditors connect applicable requirements, the evidence examined and their conclusions. Professional judgment follows a documented method.
Our audit processThe certification decision is separate from conducting the audit. Clients have access to documented complaints and appeals procedures.
Certification policiesLeadership
Complade’s leadership oversees governance, technology, audit delivery and certification management.
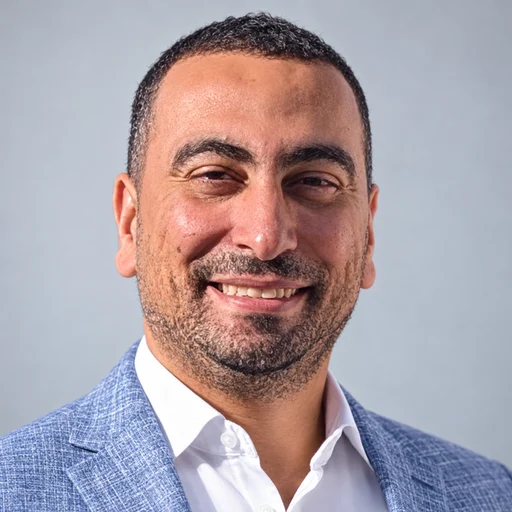
Founder and Managing Director
Leads Complade’s strategy, governance and certification operations. His career in cloud services and technology leadership began in 2008. In 2009, he and his team led a major migration from Microsoft to Google’s cloud services. His subsequent experience spans international team leadership, organizational risk oversight and certification operations.
His earlier articles are also published under the name Yehia (Ian) Ahmed.
Doctor of Business Administration (DBA) in Cybersecurity Management, University of Colorado Colorado Springs (2024); Master of Management, Smith School of Business, Queen’s University (2021); Graduate Certificate in Cybersecurity Management (2022); Bachelor of Science (BSc) in Electronics and Communications Engineering, Misr International University (MIU, 2010).
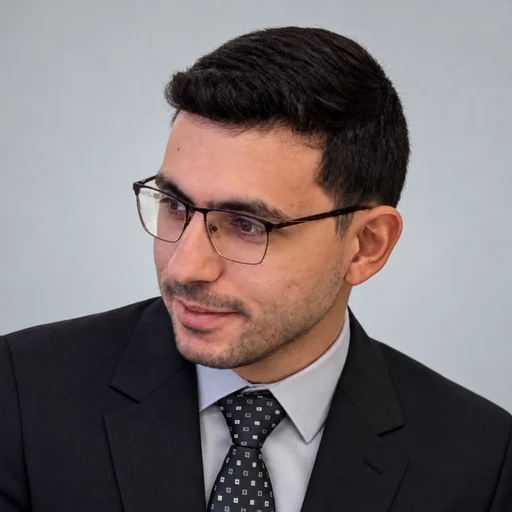
Director of Technology
Leads Complade’s technology strategy and the development of its audit portal. He brings over eight years of experience in cloud architecture, platform development and engineering leadership, with a focus on secure systems and artificial intelligence.
Bachelor of Science (BSc) in Electronics and Communication Engineering, Misr International University (MIU, 2023). Professional training in Google Cloud architecture and project management.
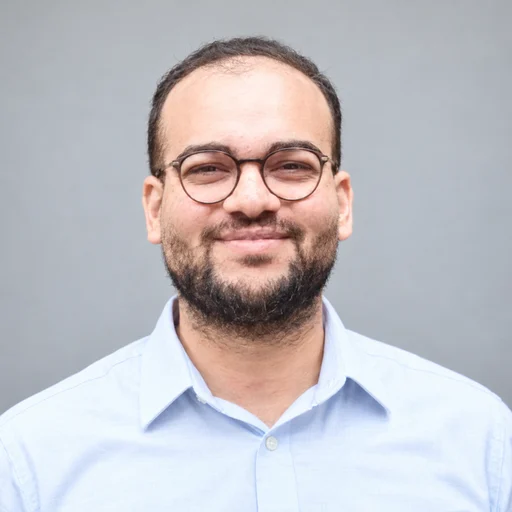
Director of Audit Delivery
Oversees audit delivery by Complade’s auditors, including planning, evidence review and report quality. His experience combines ISO/IEC 27001 and CyberSecure Canada auditing with cloud engineering, network security and artificial intelligence.
Master of Science (MSc) in Artificial Intelligence, Loughborough University (2023); Bachelor of Science (BSc) in Computer Science and Engineering, German University in Cairo (GUC, 2021). ISO/IEC 27001:2022 Lead Auditor qualification, International Board for IT Governance Qualifications (IBITGQ, 2025).
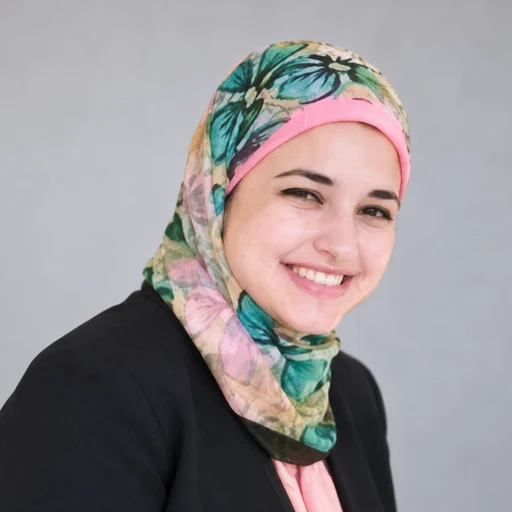
Director of Certification Services
Oversees certification processes, client-file coordination and conformance with accreditation requirements. Part of Complade’s certification team since 2024, she brings experience in service delivery management, team coordination and process improvement.
MBA (Master of Business Administration), Ain Shams University; business degree with a major in Accounting and minor in Finance, Misr International University (MIU, 2011). Qualifications in project management (PMP) and ISO/IEC 27001:2022 lead auditing.
Management, audit and certification decision responsibilities are assigned in accordance with competence and impartiality requirements. Certification decisions are made by people who did not conduct the audit concerned. Impartiality policy
Organizations bring people, processes and resources together to create value. Stakeholders need evidence of how the resulting risks are managed.
Organizations rely on interconnected services to create and deliver value. Email, financial systems, customer platforms and hosted applications depend on information moving between people, suppliers and systems.
Those dependencies extend beyond a single organization. A software provider may use cloud infrastructure, external developers and other service providers. Each relationship brings responsibilities and risks that management needs to understand.
Information security management addresses people, processes and technology within a defined scope. Cloud services are part of that environment, alongside physical locations, devices, records and other information assets.
Stakeholders need credible evidence about how those risks are managed. An independent certification audit evaluates the management system against defined requirements. Certification does not guarantee that an incident will never occur.
Complade was established to make that assurance process easier to follow. Our work connects audit conclusions to the requirements and evidence, while keeping the certification decision independent of the audit itself.
Stakeholders need to understand how an organization’s risks and controls are assessed. Independent audits provide evidence for those decisions. Management remains responsible for the risks, controls and business outcomes.
Complade's objective is to provide stakeholders with informed assurance. Our current services are independent ISO/IEC 27001 and CyberSecure Canada certification audits, with the applicable surveillance and recertification activities. We document the audit criteria, evidence and findings so stakeholders can understand the basis of the certification decision.
Complade uses a transparent, repeatable audit model grounded in established standards. The work depends on competent people, appropriate technology and documented processes:
Complade reduces unnecessary auditor variation by requiring transparent, standardized methods and clear objectives based on recognized standards.
Complade audit teams have experience with cloud and AI (artificial intelligence)-enabled technologies. They combine collaborative interviews and document reviews with direct observation, data analysis, and technical testing. The process focuses on evidence, systemic causes, and effective corrective action.
Complade uses transparent, near-real-time reporting during Stage 1 and Stage 2 audits so auditees can understand findings and supporting evidence as the audit progresses.
Complade uses a structured, risk-informed certification programme with published pricing assumptions and a repeatable audit and verification cycle. The process is grounded in recognized requirements and informed by relevant threat models and technical evidence.
Review our certification process or contact us to discuss your scope.
Complade = Compliance + Lade
Complade Inc. is a federally incorporated Canadian company registered in Ontario.
Corporations Canada · Canada’s Business Registries · Ontario Business Registry
Certification body accreditation: SCC (Standards Council of Canada) listing
 SCC (Standards Council of Canada) accreditation listing
 IAF CertSearch: active status